SafetyPublished Top storyAll news from that day
Ongoing case: Cyber-capable AI models Safety finding · 6 stories
Anthropic's OSS Scanner writes vulnerability reports without human review
Anthropic launched OSS Scanner on 8 October, an opt-in service for open-source maintainers, and says its reports are fully model-generated, without human review or triage.
Check our sources · 9 facts from 2 sources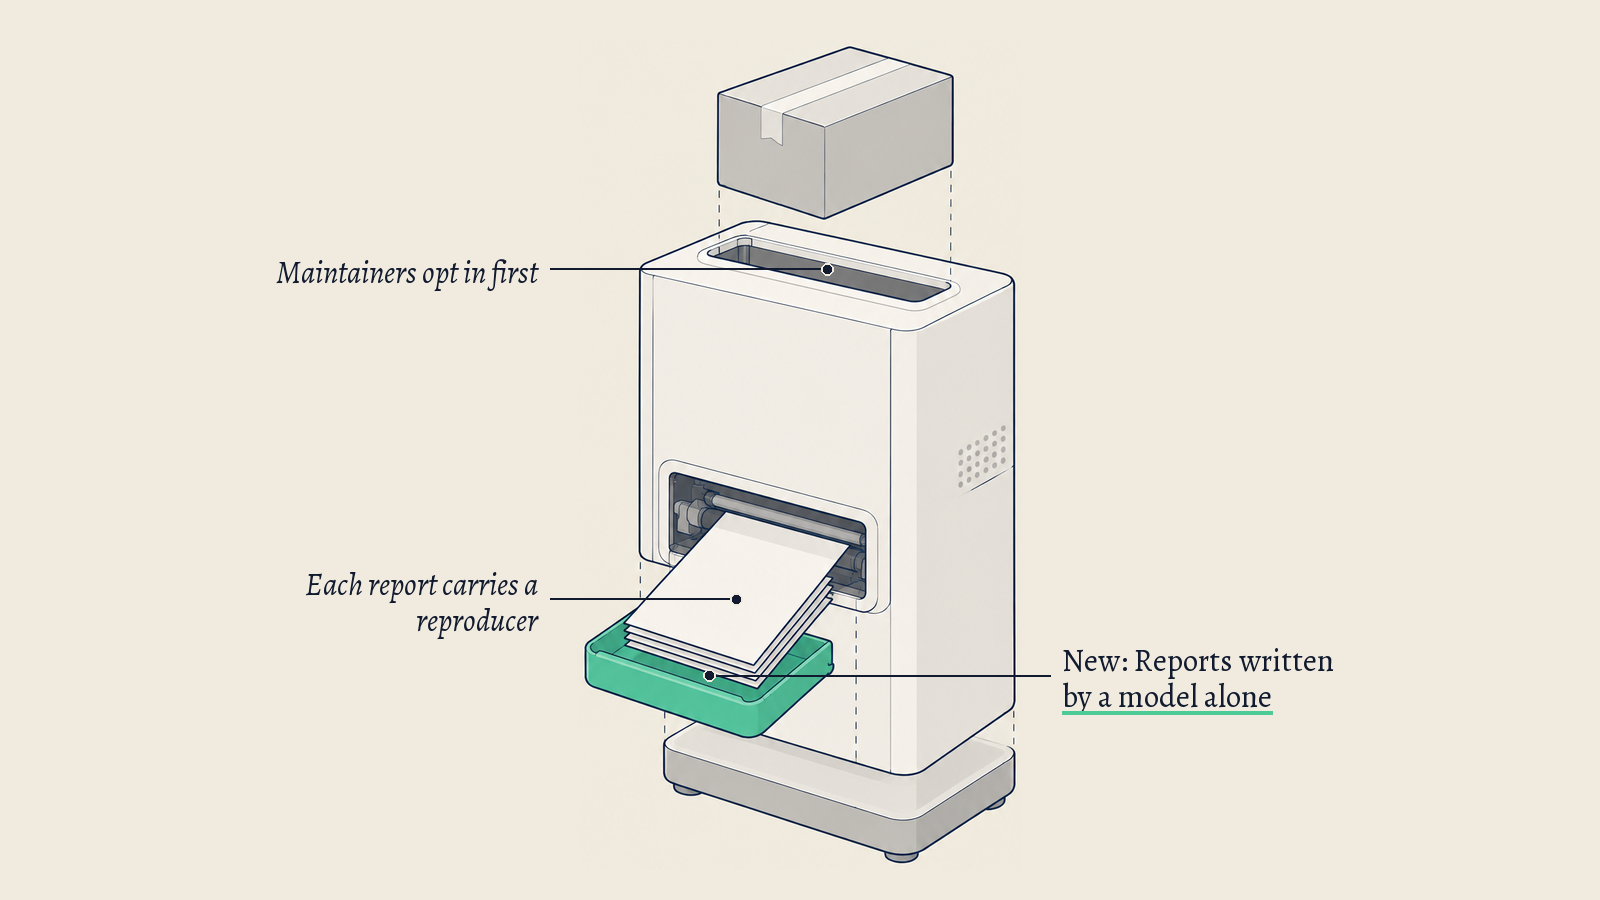 Illustration made with AI for ai notis
Key points
- Anthropic says each report includes a self-contained reproducer and an explanation, plus a bisection and a candidate patch where possible, and that the outputs are fully model-generated.
- Anthropic says expert penetration testers reviewed 97 critical and high-severity findings across 48 projects, and 85 of them met the bar for its coordinated vulnerability disclosure process.
- Anthropic's disclosure dashboard, which counts findings from all Claude models, lists 6,157 reported to maintainers as of 2 October; 4,824 were reported direct by Anthropic and may contain false positives.
What happened
Anthropic launched OSS Scanner on 8 October 2026 as an opt-in vulnerability-finding service for open-source software. Core maintainers of eligible projects enrol by submitting a pull request to Anthropic's GitHub repository. Anthropic's post says the scanner's outputs are fully model-generated, without human review or triage.
Each report includes a self-contained reproducer and an explanation of the vulnerability, with a bisection and a candidate patch where available.
Anthropic reports that expert penetration testers reviewed 97 critical and high-severity findings across 48 projects, and that 85 of them met the bar for its coordinated vulnerability disclosure process.
Anthropic's disclosure dashboard, which counts findings from all Claude models rather than OSS Scanner alone, shows as of 2 October 2026 6,157 findings reported to maintainers, of which 4,824 were reported direct to maintainers by Anthropic and, the dashboard says, may contain false positives.
The same dashboard shows 516 patched upstream. The dashboard also shows 29,439 candidate vulnerabilities, of which 6,123 were reviewed by external security firms.
Underlined sentences link to the facts we checked. Dotted words open a short explainer.
Fact 1 of 9 · from Anthropic, 8 Oct 2026
Oct 8, 2026 ... We're launching OSS Scanner, an opt-in vulnerability scanner for the open-source ecosystem informed by our experience using Claude to find vulnerabilities during Project Glasswing.
Fact 2 of 9 · from Anthropic, 8 Oct 2026
Core maintainers of eligible projects can enroll by submitting a PR to this GitHub repo following the standard project template
Fact 3 of 9 · from Anthropic, 8 Oct 2026
The outputs of this opt-in vulnerability scanner will be fully model-generated, without human review or triage. This will enable faster and more frequent scanning, but means that it is possible reports will be incorrect or invalid.
Fact 4 of 9 · from Anthropic, 8 Oct 2026
Each report contains a self-contained reproducer, explanation of the vulnerability (including a bisection to determine when the bug was introduced, where possible), and candidate patch (when available) for how the bug can be fixed.
Fact 5 of 9 · from Anthropic, 8 Oct 2026
To validate an early version of OSS Scanner, we asked the expert penetration testers who review our CVD findings to check 97 critical and high-severity vulnerabilities from the scanner across 48 projects. Of these, 85 (88%) met the bar for our CVD process. Of the remaining 12, 11 were real but duplicated known issues or other findings from the scan, and only one was invalid
Fact 9 of 9 · from Anthropic, 2 Oct 2026
Discovered Triaged 29,439 findings Candidates 6,123 findings Reviewed by external security firms
What it means for you
Our viewAnthropic says the scanner's reports are written by a model and not reviewed by a person. For a maintainer, a report is therefore a lead to check, even though Anthropic's testers found that 85 of 97 sampled critical and high-severity findings met its disclosure bar.
The dashboard figures cover Claude models in general, so they do not show how OSS Scanner itself performs. If you maintain an open-source project, read the enrolment steps before opting in and decide who will triage incoming reports.
If you depend on open-source packages, ask your suppliers how they handle machine-written reports.
It adds no new facts.
Your reaction
We count reactions per story and day, never who reacted. The counts help us choose what goes in the monthly issue. If you are signed in, your own page shows yours too.
We count reactions per story and day, never who reacted. They help choose what goes in the monthly issue.
Check our sources
Every sentence above is checked against these 2 sources.
1 An opt-in vulnerability-finding service for open-source software
Open the source archived copy-
Anthropic published an opt-in vulnerability-finding service for open-source software, OSS Scanner, in a post dated 8 October 2026.
citeOct 8, 2026 ... We're launching OSS Scanner, an opt-in vulnerability scanner for the open-source ecosystem informed by our experience using Claude to find vulnerabilities during Project Glasswing.
-
Anthropic's post says core maintainers of eligible projects enrol by submitting a pull request to Anthropic's GitHub repository.
citeCore maintainers of eligible projects can enroll by submitting a PR to this GitHub repo following the standard project template
-
Anthropic's post says the scanner's outputs are fully model-generated, without human review or triage.
citeThe outputs of this opt-in vulnerability scanner will be fully model-generated, without human review or triage. This will enable faster and more frequent scanning, but means that it is possible reports will be incorrect or invalid.
-
Anthropic's post says each report includes a self-contained reproducer and an explanation of the vulnerability, and, where possible, a bisection showing when the bug was introduced and a candidate patch.
citeEach report contains a self-contained reproducer, explanation of the vulnerability (including a bisection to determine when the bug was introduced, where possible), and candidate patch (when available) for how the bug can be fixed.
-
Anthropic's post says expert penetration testers reviewed 97 critical and high-severity findings across 48 projects, and 85 of them met the bar for its coordinated vulnerability disclosure process.
citeTo validate an early version of OSS Scanner, we asked the expert penetration testers who review our CVD findings to check 97 critical and high-severity vulnerabilities from the scanner across 48 projects. Of these, 85 (88%) met the bar for our CVD process. Of the remaining 12, 11 were real but duplicated known issues or other findings from the scan, and only one was invalid
2 Anthropic's coordinated vulnerability disclosure dashboard
Open the source archived copy-
Anthropic's disclosure dashboard, as of 2 October 2026, lists 6,157 findings reported to maintainers.
citeAs of October 2, 2026, we've disclosed 6,157 vulnerabilities across 591 open source projects. ... 6,157 findings Total reported to maintainers
-
The dashboard lists 4,824 of those findings as reported direct to maintainers by Anthropic, marked as possibly containing false positives.
Toned down to what the source says
cite4,824 findings Reported direct to maintainers by Anthropic May contain false positives
-
The dashboard lists 516 findings patched upstream.
citeTo our knowledge, 516 of these have been patched. ... 516 findings Patched upstream
-
The dashboard lists 29,439 candidate vulnerabilities, of which 6,123 were reviewed by external security firms.
citeDiscovered Triaged 29,439 findings Candidates 6,123 findings Reviewed by external security firms
Every sentence above is checked against these 2 sources. Each fact has its own address you can cite.
Source 1 · Anthropic · 8 Oct 2026
An opt-in vulnerability-finding service for open-source software
Anthropic published an opt-in vulnerability-finding service for open-source software, OSS Scanner, in a post dated 8 October 2026.
Oct 8, 2026 ... We're launching OSS Scanner, an opt-in vulnerability scanner for the open-source ecosystem informed by our experience using Claude to find vulnerabilities during Project Glasswing.
Anthropic's post says core maintainers of eligible projects enrol by submitting a pull request to Anthropic's GitHub repository.
Core maintainers of eligible projects can enroll by submitting a PR to this GitHub repo following the standard project template
Anthropic's post says the scanner's outputs are fully model-generated, without human review or triage.
The outputs of this opt-in vulnerability scanner will be fully model-generated, without human review or triage. This will enable faster and more frequent scanning, but means that it is possible reports will be incorrect or invalid.
Show all 5 factsShow fewer facts
Anthropic's post says each report includes a self-contained reproducer and an explanation of the vulnerability, and, where possible, a bisection showing when the bug was introduced and a candidate patch.
Each report contains a self-contained reproducer, explanation of the vulnerability (including a bisection to determine when the bug was introduced, where possible), and candidate patch (when available) for how the bug can be fixed.
Anthropic's post says expert penetration testers reviewed 97 critical and high-severity findings across 48 projects, and 85 of them met the bar for its coordinated vulnerability disclosure process.
To validate an early version of OSS Scanner, we asked the expert penetration testers who review our CVD findings to check 97 critical and high-severity vulnerabilities from the scanner across 48 projects. Of these, 85 (88%) met the bar for our CVD process. Of the remaining 12, 11 were real but duplicated known issues or other findings from the scan, and only one was invalid
Source 2 · Anthropic · 2 Oct 2026
Anthropic's coordinated vulnerability disclosure dashboard
Anthropic's disclosure dashboard, as of 2 October 2026, lists 6,157 findings reported to maintainers.
As of October 2, 2026, we've disclosed 6,157 vulnerabilities across 591 open source projects. ... 6,157 findings Total reported to maintainers
The dashboard lists 4,824 of those findings as reported direct to maintainers by Anthropic, marked as possibly containing false positives.
Toned down to what the source says4,824 findings Reported direct to maintainers by Anthropic May contain false positives
The dashboard lists 516 findings patched upstream.
To our knowledge, 516 of these have been patched. ... 516 findings Patched upstream
Show all 4 factsShow fewer facts
The dashboard lists 29,439 candidate vulnerabilities, of which 6,123 were reviewed by external security firms.
Discovered Triaged 29,439 findings Candidates 6,123 findings Reviewed by external security firms
Topics
The morning email
On the mornings we publish: the three top stories and up to four short ones. Free.
We email you a link to confirm. An issue may include one sponsor, always labelled Sponsored · Advertisement. Our emails count opens and clicks, not who made them. Unsubscribe in one click. What we keep