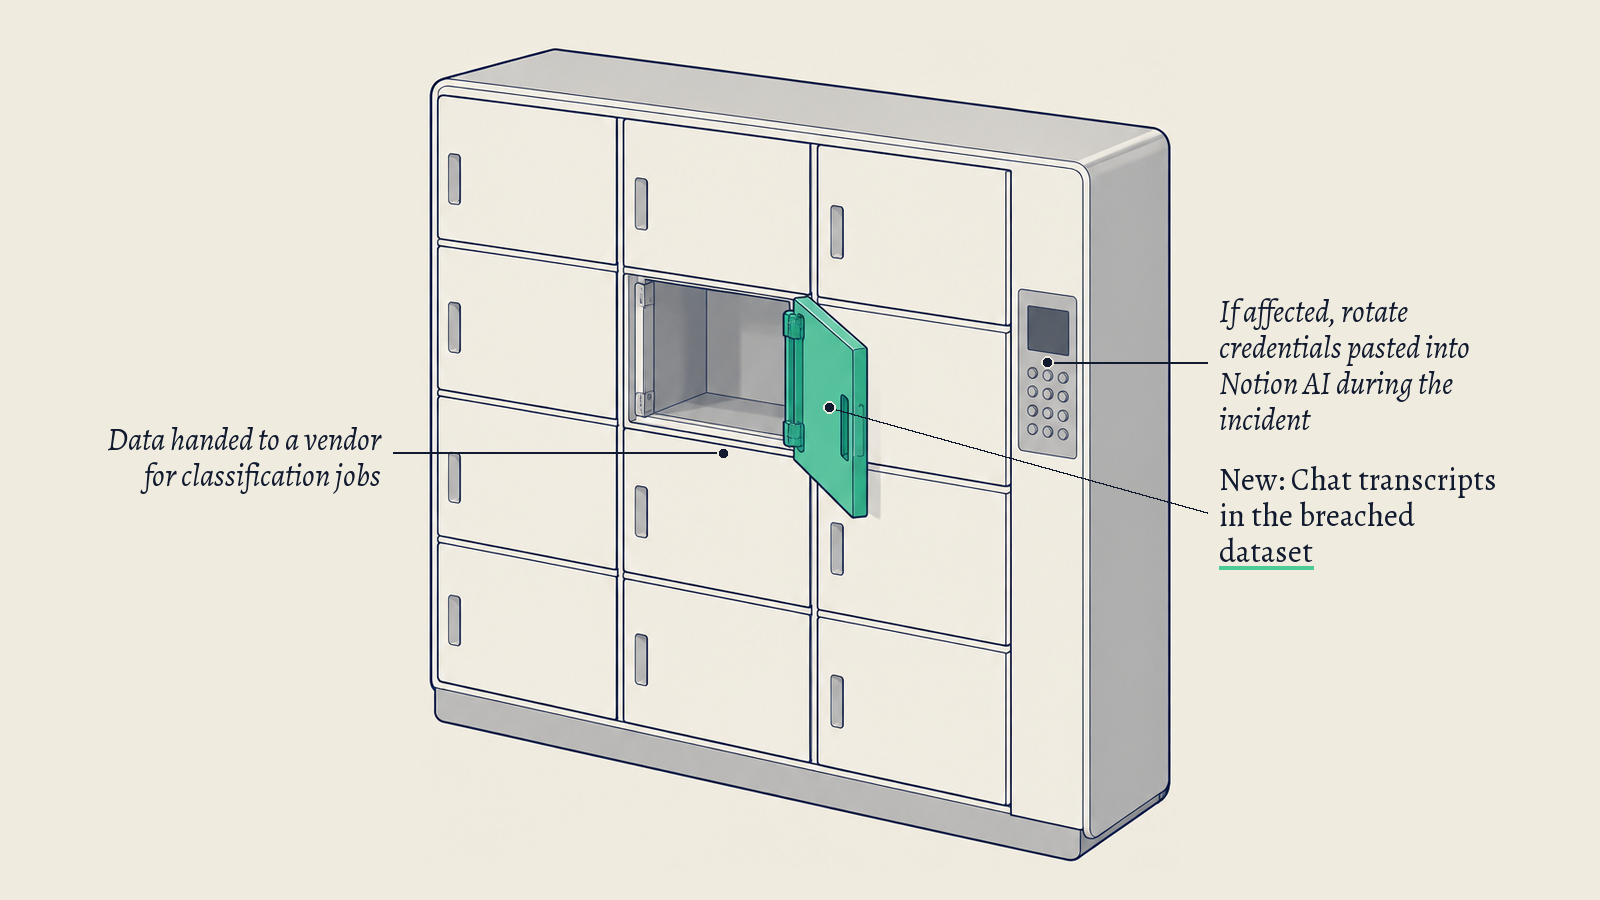
- Notion says the Fireworks AI incident affects fewer than 1% of its workspaces, and that the dataset included Notion AI chat transcripts used for its Insights feature.
- Fireworks says it also found impact to account and billing information and, for a limited set of accounts, to secrets, datasets and incomplete model weights, without giving a number.
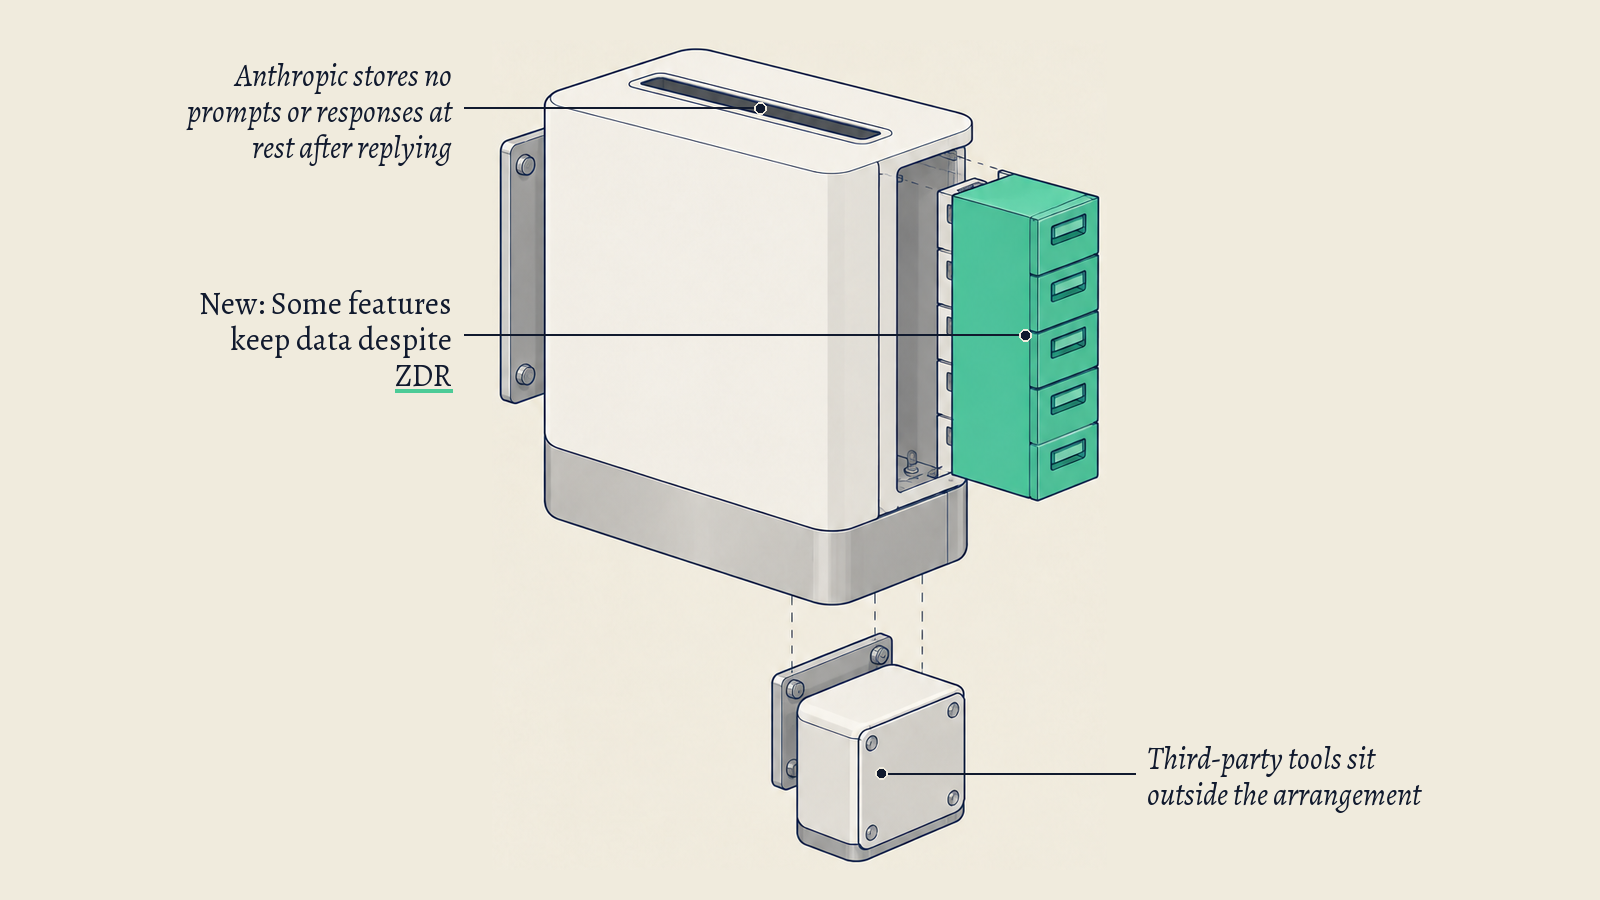
- Fireworks says it has not detected impact to Inference, Training SDK and Nexus, on its investigation to date; the data was reached through an internal application.
Notion says fewer than 1% of its workspaces were affected after attackers accessed data held by its AI vendor Fireworks AI, including Notion AI chat transcripts used for its Insights feature. Notion's security advisory, updated on 12 November, says the transcripts for most affected workspaces are unattributable: they carry no author or workspace label and no tool call results.
Fireworks' own bulletin has grown since its first version of 9 October, which said only secrets used in evaluation jobs were known to be accessed. Its update of 9 November says the intruders also reached account and billing information, and, for a limited set of accounts, secrets, datasets and incomplete model weights. Fireworks says payment card numbers are not stored and were not affected, and it does not give a number of affected accounts.
Fireworks says the evidence links the attack to a financially motivated group that aims to sell tokens from unauthorised access to large language models, known as LLMJacking. It also says a third-party cloud provider that hosted its R&D machines had an incident on 23 October, and that on 24 October the attacker used it to reach development machines and run a workload that led to more customer data being affected.
Notion's timeline starts on 2 November, when Fireworks first told it a small set of data had been accessed. On investigation, Notion says, that dataset included Notion AI synthetic testing data, and no Notion AI customer data was involved. By 3 November Notion had disconnected from Fireworks. On 6 November Fireworks said customer data may have been involved, and on 8 November it confirmed the final dataset. Notion contacted affected customers on 9 November and revoked exposed Notion API keys found in the affected messages on 11 November.
Notion tells affected customers to treat the data as exposed and to rotate any passwords or API keys they pasted into Notion AI. It has switched off Insights and stopped serving open-weight models through Fireworks. Fireworks tells affected customers to replace revoked keys and rotate third-party credentials with the issuing providers.
Fireworks says it has not detected any impact to Inference, Training SDK and Nexus, which it describes as zero data retention by default, on its investigation to date. The affected internal application provided access to resource metadata, billing information and, for certain customers, a subset of incomplete model weights and datasets. Neither company says an AI model was used in the attack.
What it means for you Our view
Both companies address the advice to affected customers. Notion tells them to treat the data as exposed and to rotate any passwords, API keys or other credentials pasted into Notion AI, and Fireworks tells them to replace revoked keys and rotate third-party credentials with the providers that issued them. Fireworks says the evidence links the attack to a group that sells stolen access to large language models; neither company says an AI model was used in it. If you have been notified, rotate those credentials first. If not, ask your team where credentials get pasted into AI tools.
TAGSFireworks AINotionNotion AI