CISA urges immediate patching of OpenJDK flaw on x86-64 CPUs with AVX-512 VBMI
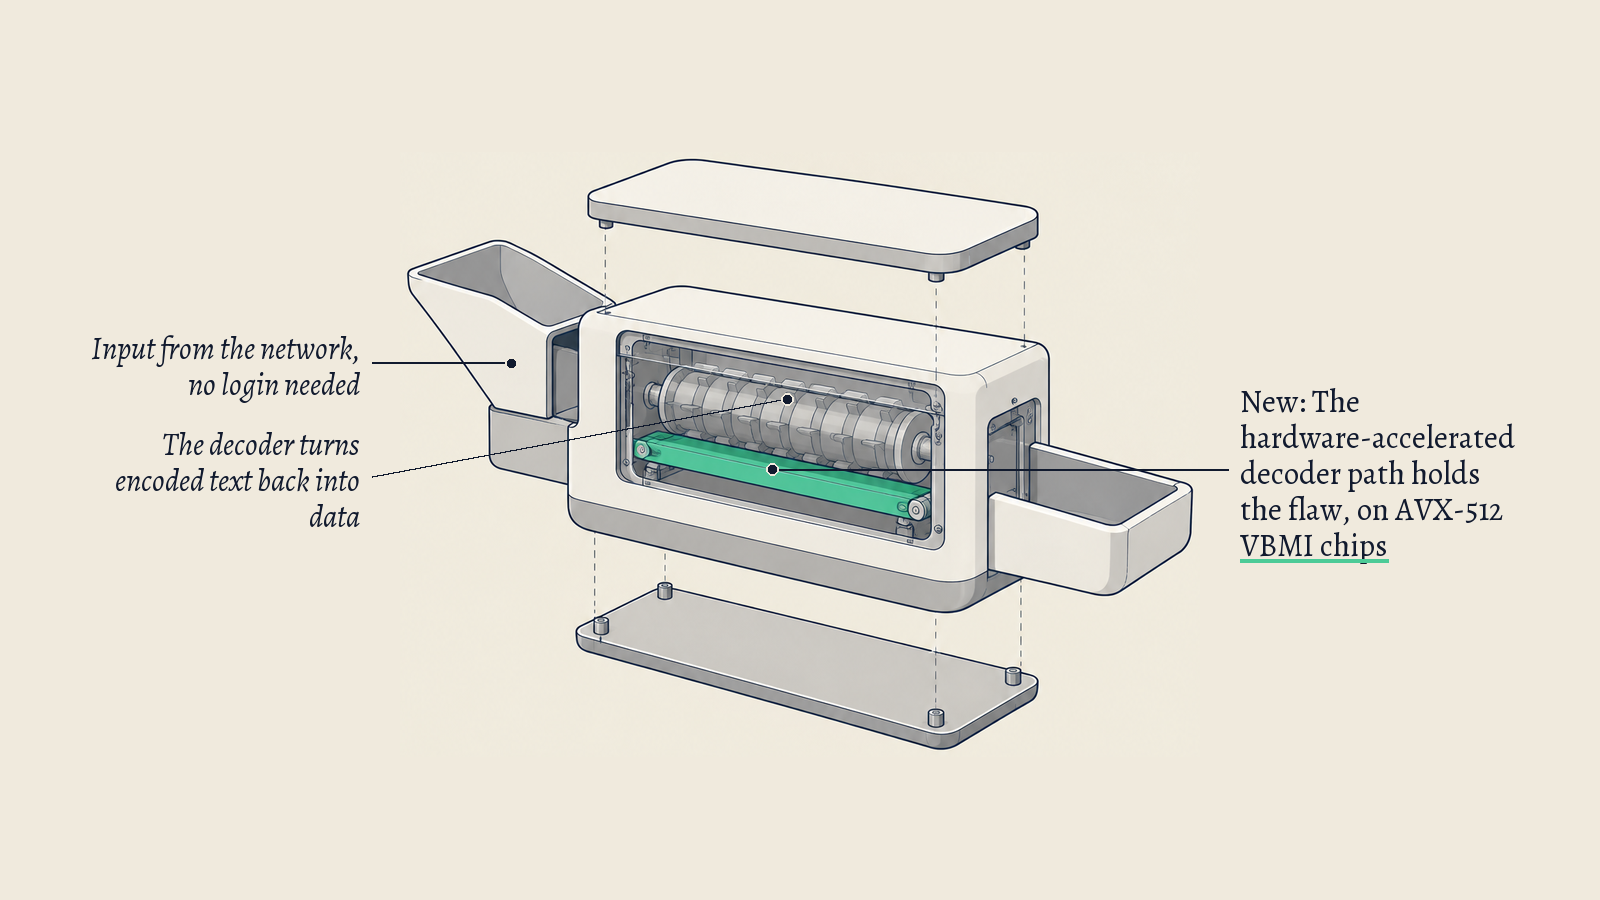 Illustration made with AI for ai notis
Calif says an attacker with no credentials can reach code execution and that it directed Codex to find and weaponize the flaw; Wiz says its Wiz Atlas AI harness built an exploit.
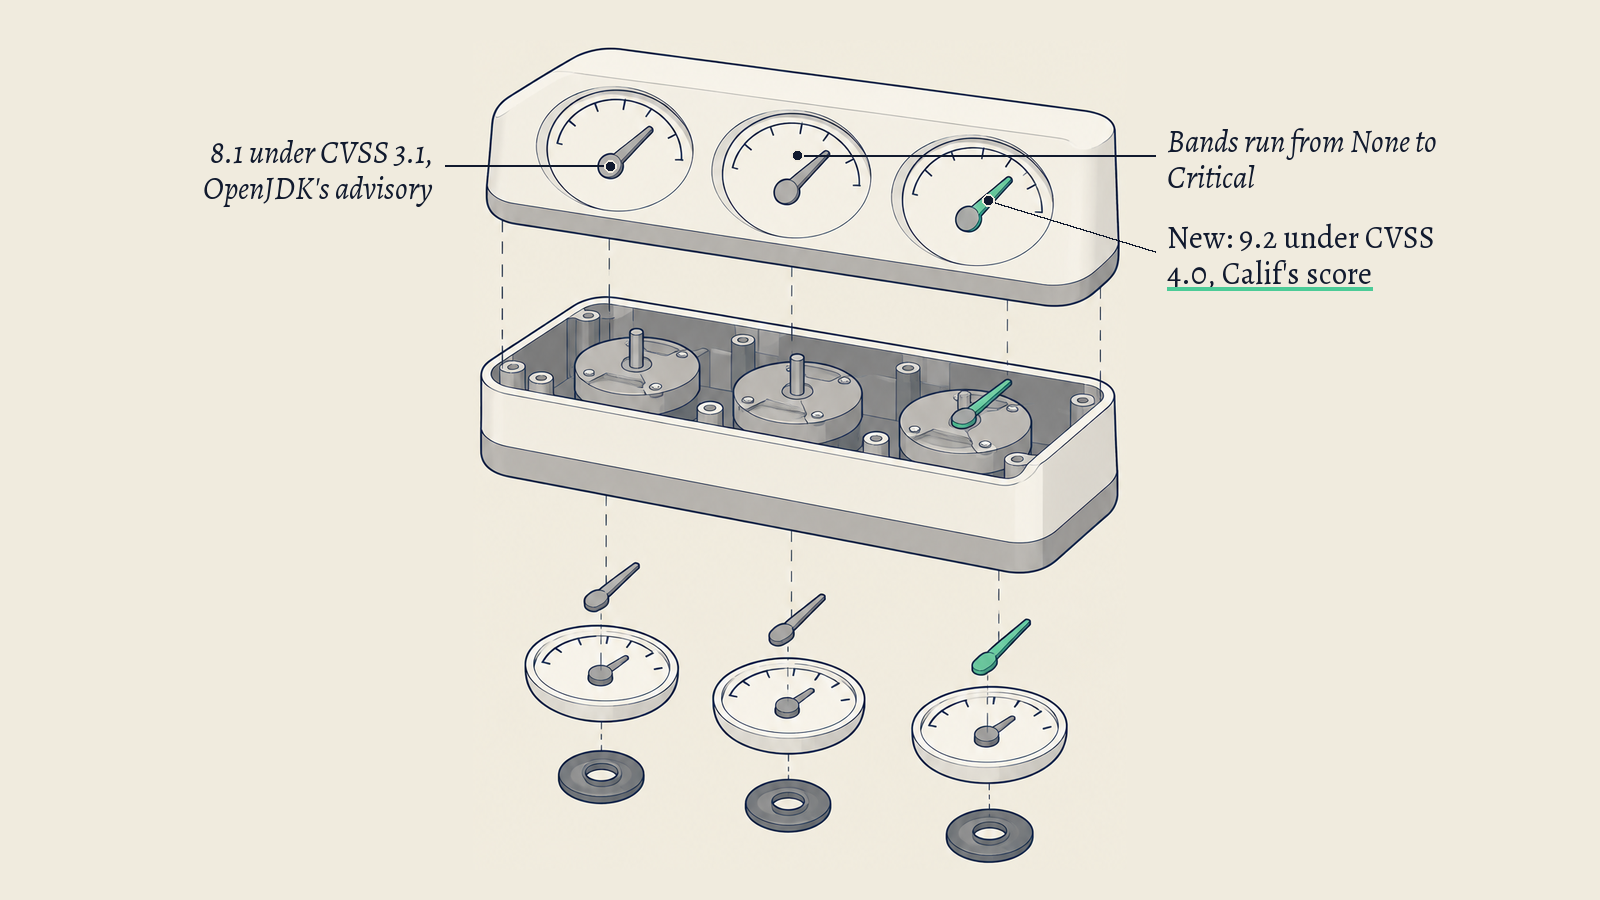
- CISA's alert of 17 November strongly urges immediate patching; CERT-EU rates the flaw high, with a CVSS score of 8.1, and Calif scores it 9.2, Critical.
- CERT-EU says exploitation needs an x86-64 CPU with AVX-512 VBMI, such as Intel Ice Lake or later or AMD Zen 4 or later, and attacker-controlled Base64 data reaching the decoder.
- CERT-EU lists fixes in Java SE and OpenJDK 17.0.21 patch 1, 21.0.13 patch 1 and 25.0.5 patch 1; OpenJDK-based distributions release fixes on their own schedules.
Teams that run Java on x86-64 servers with AVX-512 VBMI processors should update OpenJDK now. Calif, a security firm, disclosed a flaw it calls Java4Shell (CVE-2026-114938) on 17 November 2026: a memory-corruption bug in OpenJDK's Base64 decoder that lets a remote attacker with no credentials overwrite heap memory and reach remote code execution.
OpenJDK published its vulnerability advisory the same day, and Calif says Oracle released a patch at the same time. The advisory fixes ten OpenJDK issues in total, and it lists CVE-2026-114938 in the HotSpot compiler with a CVSS 3.1 base score of 8.1. Calif scores the flaw 9.2 out of 10, Critical, under CVSS 4.0. CISA's alert of 17 November says it strongly urges organisations to patch immediately, and CERT-EU's advisory 2026-021 of 18 November rates the flaw high severity, CVSS 8.1. CISA's Known Exploited Vulnerabilities catalogue, in the feed released on 17 November with 1,782 entries, does not list it.
The bug affects OpenJDK 17.0.6 and newer, and the distributions built from it, but only on x86-64 processors that support AVX-512 VBMI; Wiz and CERT-EU say ARM64 is not affected. Calif says it demonstrated remote code execution, in default configurations, against Keycloak, Atlassian Jira and Confluence, JFrog Artifactory, Jenkins and PingFederate without logging in, and against Kafka, Solr, Elasticsearch, Gerrit and Spinnaker after login.
If patching has to wait, CERT-EU says to disable the intrinsic with the JVM options -XX:+UnlockDiagnosticVMOptions -XX:-UseBASE64Intrinsics, or alternatively -XX:UseAVX=2, which can reduce performance; both need a JVM restart. Calif says to use the second flag only on x86-64 hosts, because OpenJDK on ARM does not recognise it and will fail to start. Wiz advises patching externally facing packaged Java applications first.
Calif says there is no universal exploit; each target needs its own approach. It published a proof of concept that triggers the memory corruption safely, and says it is holding back its application-specific exploits until people have had time to upgrade.
Calif says it used AI to find and weaponize the flaw. Its researcher Quang Luong told Codex to audit HotSpot's compiler, intrinsics, widely used APIs and cryptography, and Calif says it took an hour to find the bug and two more hours to build the first working exploit, at a token cost under $200. Calif does not name a Codex model version. Wiz says its own AI research harness, Wiz Atlas, found and built a proof-of-concept exploit within two hours, before the full details were public.
What it means for you Our view
If you run OpenJDK or any Java runtime bundled in third-party software or container images, update it now, internet-facing systems first, as CISA asks. If you cannot update at once, CERT-EU says to start the JVM with -XX:+UnlockDiagnosticVMOptions -XX:-UseBASE64Intrinsics, or with -XX:UseAVX=2, which can reduce performance; Calif says to apply that second flag only on x86-64 hosts, because OpenJDK on ARM does not recognise it and will fail to start. Both need a JVM restart. Calif says there is no universal exploit and that it is holding back product-specific ones, which gives time to patch but not a reason to wait. Start with an inventory of which hosts have AVX-512 VBMI processors and which products carry their own Java.